Skip to content

Certifications and compliance

Standards that shape the way we work.

For our size, we hold an unusually wide range of audited standards and frameworks. For each one we show what it means for the project, security and operations - not just the logo.

What are you dealing with?

01

Information security

How we protect your data, access and systems.

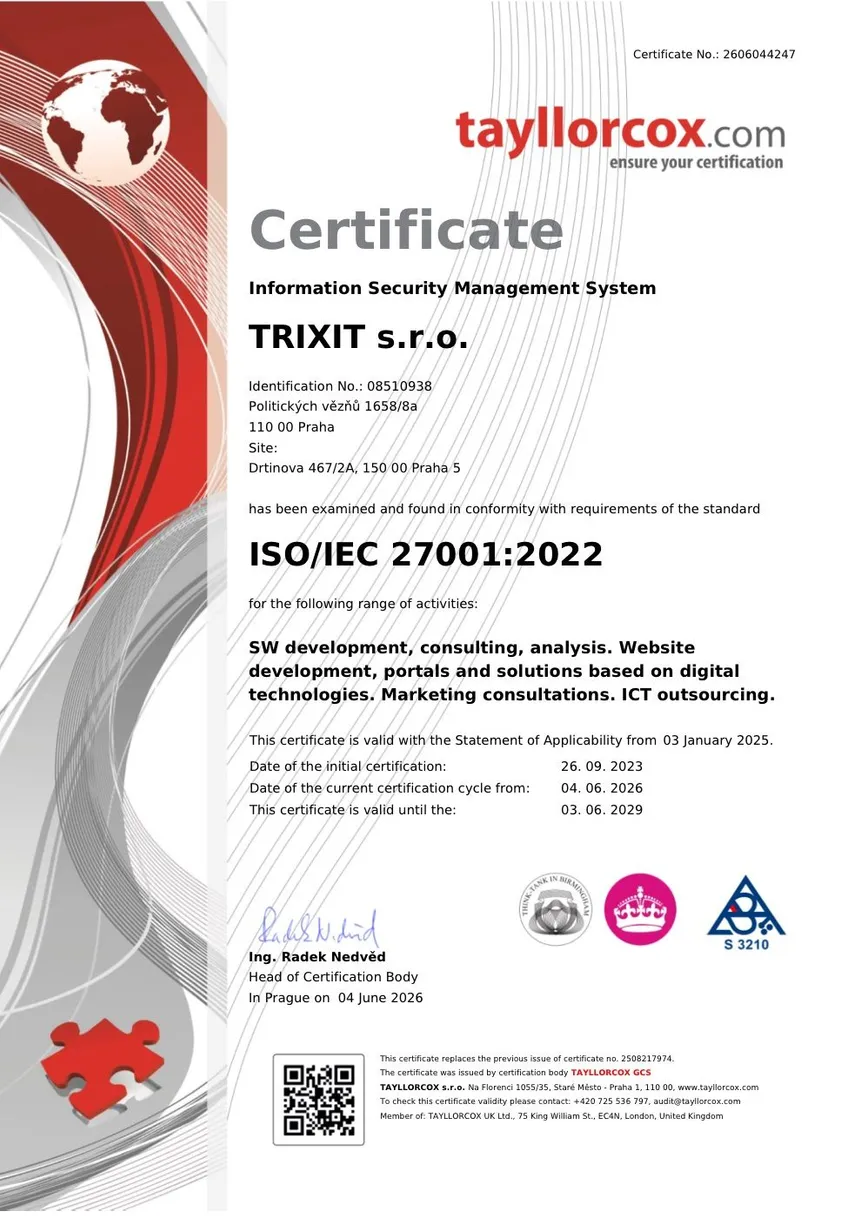
ISO 27001

Information security management

Access, risks and incidents are managed under audited rules. You know who may access what, how risks are assessed and what happens in a security event.

When it mattersSupplier security reviews, enterprise procurement, regulated environments and projects with confidential data.
Certificate (PDF)

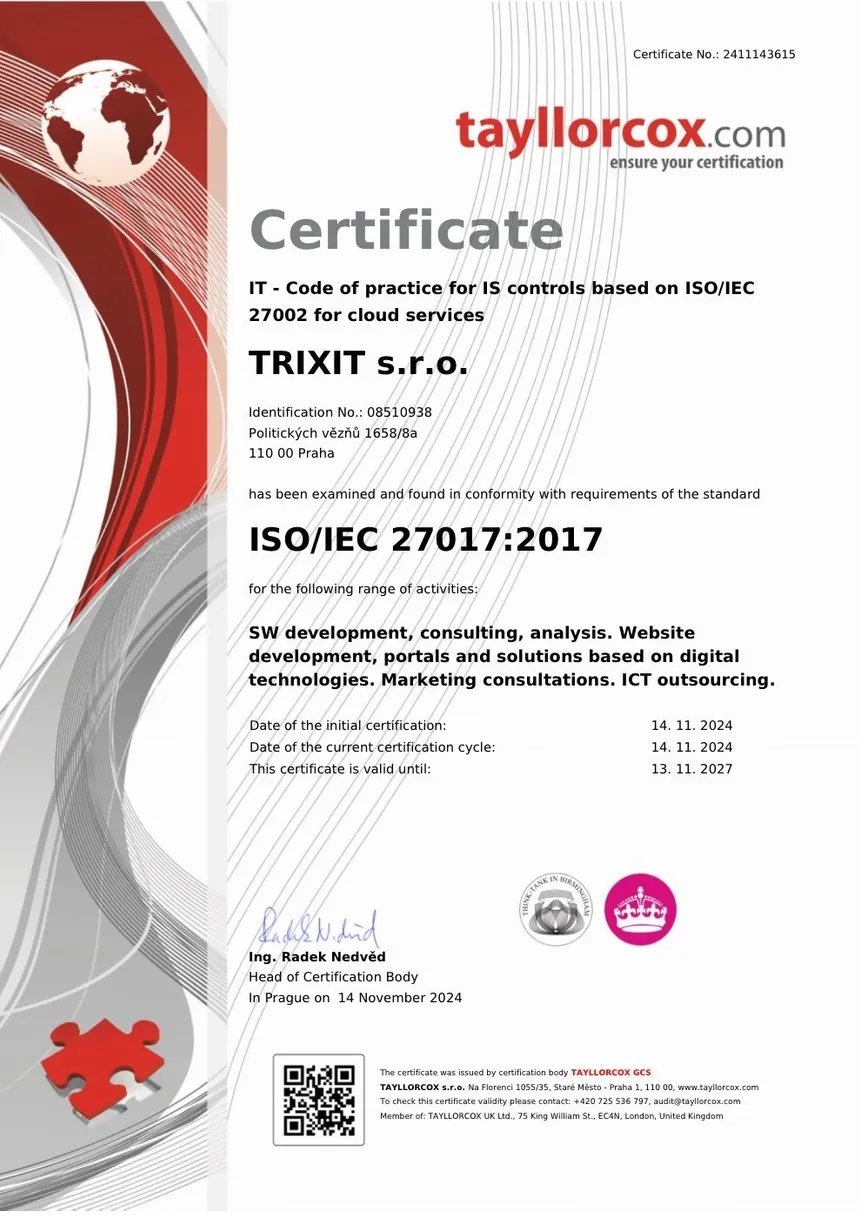
ISO 27017

Cloud service security

For the cloud we have additional security controls and a written split of duties between the cloud provider, us and you.

When it mattersApplications running in Azure, AWS or another cloud, and security questionnaires on cloud services.
Certificate (PDF)

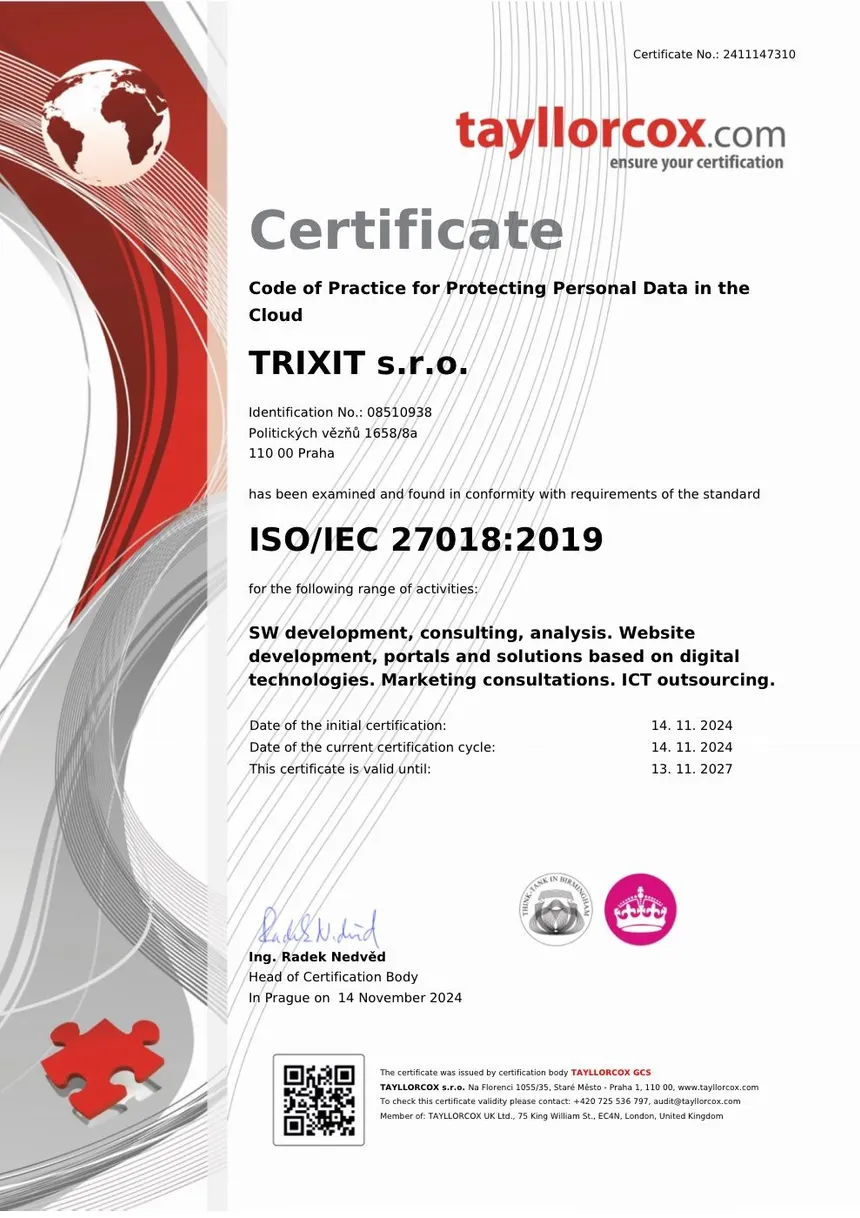
ISO 27018

Personal data protection in the cloud

It is documented where personal data is stored, who can access it and how it is handled. And we can prove all of it.

When it mattersGDPR, data processing agreements and systems that handle customer or employee data in the cloud.
Certificate (PDF)

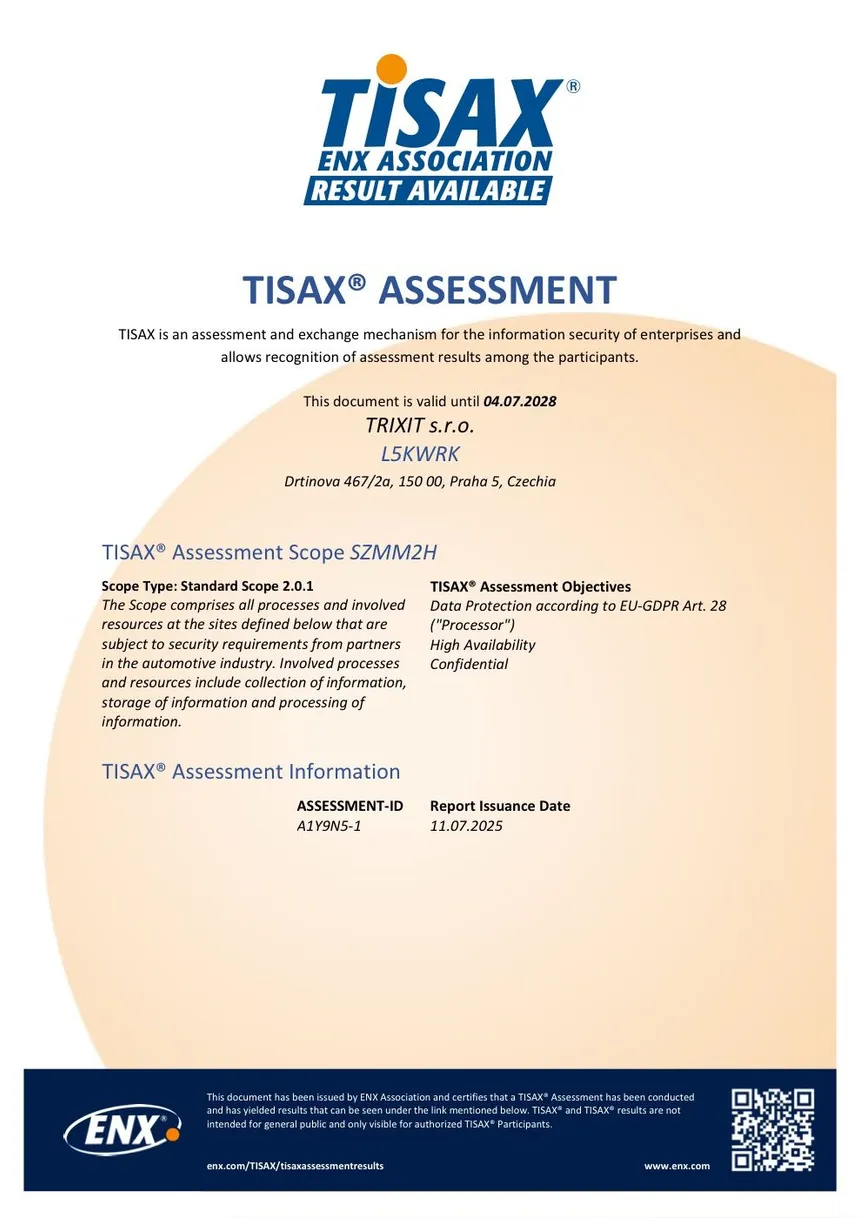
TISAX

Security assessment for automotive

We have passed the information security assessment the automotive industry requires, and we handle manufacturer data in a separate regime.

When it mattersWork with car makers and their suppliers, design and prototype documentation, sharing results via ENX.
Certificate (PDF)
02

Quality and delivery

How we run projects and operations so the result never depends on chance.

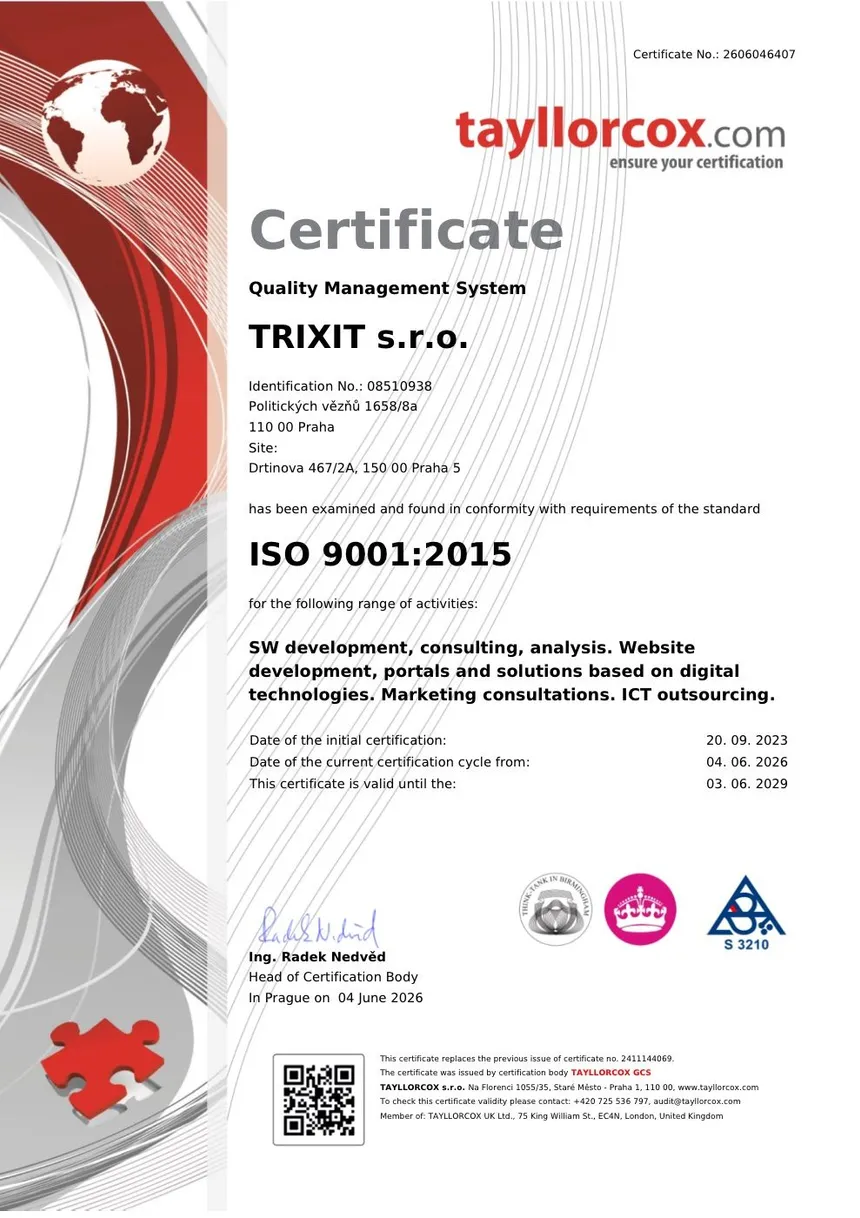
ISO 9001

Quality management system

Procedures, checkpoints and documentation are described and audited. The project does not depend on individuals, and handovers or team changes run smoothly.

When it mattersLong-term delivery, your internal audit and whenever you ask whether people can be replaced.
Certificate (PDF)

ISO 10006

Quality management in projects

Each phase has predefined outputs and acceptance criteria. You know what you will get and how to tell it is done.

When it mattersPhased budget drawdown, PMO, multi-vendor management and projects with formal acceptance.
Certificate (PDF)

ISO 20000

IT service management

We run operations with agreed service levels, request tracking and change management. Every intervention is logged with a clear escalation path.

When it mattersApplications in production, contractual availability and maintenance windows, evidence for your own audit.
Certificate (PDF)
03

Continuity and responsibility

How we keep services stable and run our own operations responsibly.

ISO 22301

Business continuity management

Our business continuity plans are prepared and regularly tested. Services run reliably and you know in advance how we ensure their recovery.

When it mattersCritical and 24/7 operations, supplier assessment under NIS2 and DORA, contracts with RTO and RPO requirements.
Certificate (PDF)

ISO 14001

Environmental management

We manage the environmental impact of our own operations in an audited system, and legal compliance is backed by a certificate, not a statement.

When it mattersESG reporting, supply-chain assessment and tenders with environmental criteria.
Certificate (PDF)

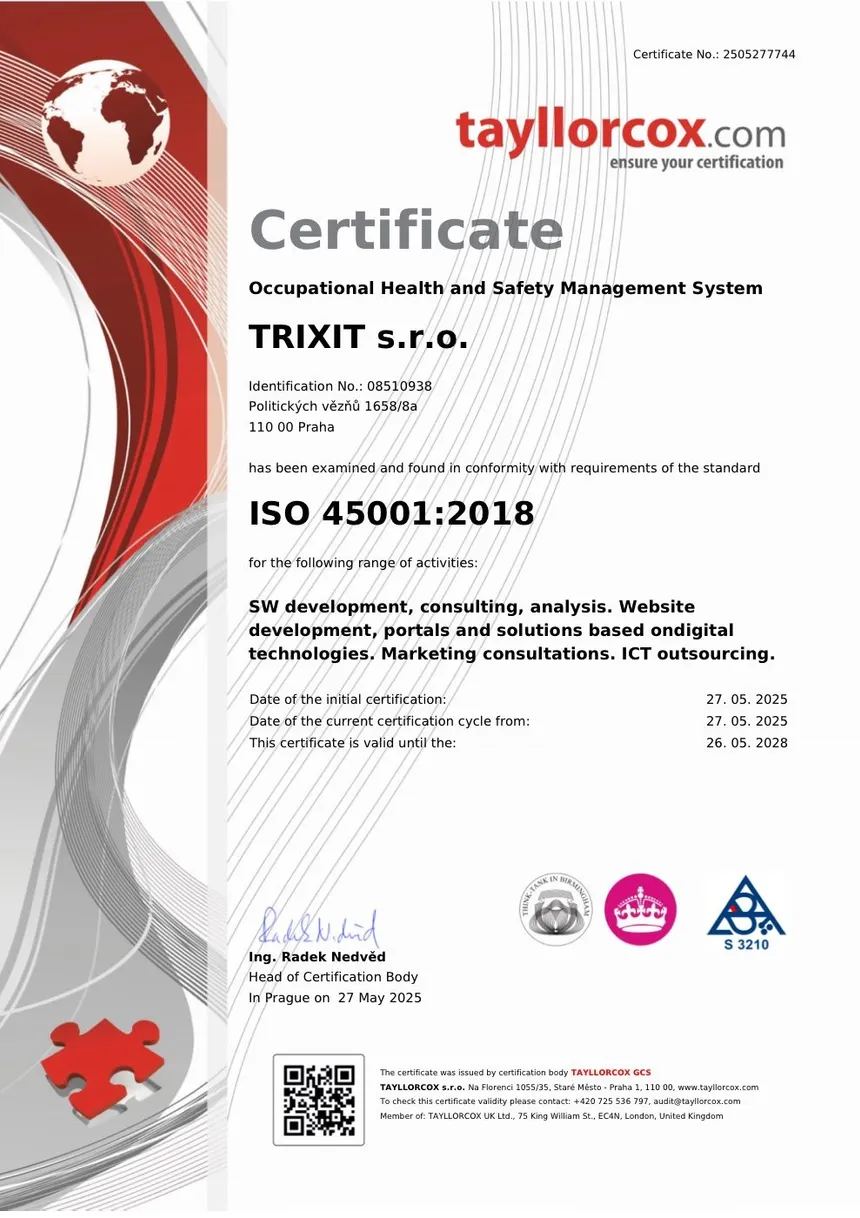
ISO 45001

Occupational health and safety

We manage occupational health and safety in an audited system, including rules for our people working outside the office.

When it mattersWork on customer premises, corporate supplier questionnaires and tenders with OHS criteria.
Certificate (PDF)